API Version Debt: How Untracked Deprecations Are Quietly Detonating Your Production Stack
Photo: Esther Tulodetzki, CC BY-SA 3.0 de, via Wikimedia Commons
There is a particular kind of production incident that engineering teams dread most — not the ones that announce themselves loudly through obvious misconfigurations or failed deployments, but the ones that materialize silently, weeks or months after the original decision that caused them. API version debt belongs firmly in that category.
Across US engineering organizations of every size, the operational cost of managing multiple API versions simultaneously is consistently underestimated at the planning stage and aggressively felt at the incident stage. The pattern is familiar: a third-party service updates its API, a deprecation notice lands in someone's inbox, gets triaged as low priority, and disappears into a backlog. Six months later, a production endpoint begins returning malformed responses. The on-call engineer spends three hours tracing the failure back to a version sunset that was announced before the current sprint cycle even existed.
This is not an edge case. It is an operational norm for teams that have not built structured processes around API dependency management.
Why API Versioning Creates Compounding Maintenance Costs
The surface-level problem with API versioning is straightforward: external services change, and your integration layer must change with them. The deeper problem is that most engineering teams treat API version management as an event-driven activity rather than a continuous one. They respond to deprecation notices when they surface, rather than proactively auditing their dependency landscape on a scheduled cadence.
This reactive posture creates compounding costs in at least three distinct ways.
First, there is the migration debt itself. Every API version your codebase depends on that is not the current stable release represents deferred migration work. The longer that work is deferred, the more entangled the legacy integration becomes with surrounding business logic. What might have been a two-day migration at the point of initial deprecation announcement can easily become a two-week refactor by the time the sunset deadline arrives — particularly if the API in question has been wrapped in multiple service layers or consumed by several independent modules.
Second, there is the testing surface problem. Older API versions frequently return subtly different data shapes, error codes, or pagination behaviors than their successors. If your test suite was written against a specific version's contract and has not been updated to account for version-specific behavior, you may be running green builds against assumptions that no longer reflect reality in production. This is one of the more insidious forms of false confidence in the software delivery process.
Third, there is the organizational knowledge problem. API integration details tend to live in the heads of the engineers who built them. When those engineers rotate to other teams or leave the organization, the institutional knowledge of which version is in use, why a specific version was pinned, and what downstream systems depend on a particular response format frequently leaves with them. What remains is undocumented integration behavior that nobody wants to touch.
The Fragmentation Scenario That Breaks Production
Consider a moderately complex SaaS platform that integrates with a payment processor, a CRM, a data enrichment service, and two internal microservices that each expose their own versioned APIs. Over eighteen months of active development, the following situation evolves organically:
- The payment processor integration was built against v2 of their API. v3 was released fourteen months ago. The migration was scoped but never prioritized.
- The CRM integration was updated to v4 by a contractor six months ago. The internal documentation still references v3.
- The data enrichment service deprecated v1 and v2 endpoints with a ninety-day notice. The notice was acknowledged. The migration was not completed before the deadline.
- One internal microservice exposes v1 and v2 of its own API. Three consuming services use v1. One uses v2. There is no registry documenting which is which.
None of these situations is catastrophic in isolation. In aggregate, they represent a fragile integration layer where any one of these version dependencies can detonate without warning — and where diagnosing the failure requires institutional knowledge that may not be available during an incident.
This is the version fragmentation scenario that breaks production. Not a single missed update, but an accumulation of deferred migrations, undocumented pins, and expired assumptions that collectively form a minefield underneath an otherwise functional system.
Building an API Dependency Audit Framework
Addressing API version debt requires treating it with the same operational seriousness as dependency vulnerability management or infrastructure drift. The following framework provides a starting point for teams looking to bring structure to the process.
Step one: Inventory every external and internal API dependency. This sounds obvious, but most teams lack a single authoritative list of the APIs their systems consume, the versions in use, and the deprecation status of those versions. Begin by instrumenting your codebase and infrastructure to surface this data systematically. API gateway logs, service mesh telemetry, and static analysis of your integration layer can all contribute to a comprehensive inventory.
Step two: Establish deprecation tracking as a first-class process. Assign ownership for monitoring deprecation announcements from every external API provider your organization depends on. This is not a task that should live in a shared inbox. It requires a named owner, a defined escalation path, and integration into your team's sprint planning or backlog grooming process.
Step three: Define migration SLAs based on risk tier. Not every deprecated API endpoint carries the same risk profile. A payment processor API deprecation warrants a different urgency level than a minor analytics endpoint. Categorize your API dependencies by business criticality and establish migration timelines that reflect that tiering. A reasonable default: critical integrations should be migrated within thirty days of deprecation announcement; standard integrations within ninety days.
Step four: Automate version drift detection. Several developer tooling platforms now offer automated monitoring for API contract changes, including breaking change detection and version sunset alerting. Incorporating these tools into your CI/CD pipeline means that version drift is caught during the build process rather than discovered in production. This is a force multiplier for teams that cannot dedicate significant manual effort to API monitoring.
Step five: Document version pins with expiration context. Any time your codebase explicitly pins to a specific API version — whether for compatibility, stability, or contractual reasons — that pin should be accompanied by documentation explaining why the pin exists and what the migration path looks like. Treat undocumented version pins as technical debt that must be resolved before the relevant codebase can be considered production-ready.
The Organizational Shift That Makes This Sustainable
The technical steps above are necessary but not sufficient. The deeper issue is that API version management tends to be treated as infrastructure work — important but not urgent, visible only when it fails. Making it sustainable requires an organizational shift in how version debt is perceived and prioritized.
Engineering leaders in particular need to advocate for API dependency audits as a recurring operational activity, not a one-time cleanup project. The cost of a production incident caused by an expired API integration — measured in engineering hours, customer impact, and incident response overhead — consistently exceeds the cost of proactive migration by a significant margin. Framing API version debt in those economic terms tends to accelerate its prioritization.
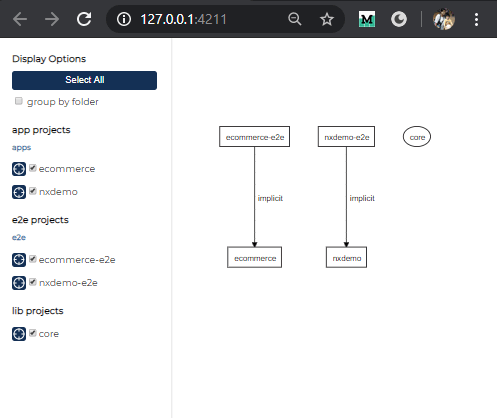
For teams building on top of developer tooling platforms, the infrastructure already exists to make this more manageable. API contract testing tools, dependency graph visualizers, and automated changelog monitoring can reduce the manual burden substantially. The gap is rarely tooling availability — it is the operational discipline to use those tools consistently.
API version debt does not announce itself. It accumulates quietly, one deferred migration at a time, until the production incident that makes it visible. The teams that avoid that incident are the ones that decided to audit their integration layer before the deadline arrived.